Your AI Agent Made a Public GitHub Repo to Show Your Reviewer a Screenshot. Check Your Developers' Personal Accounts.
Security firm Glow found more than 13,000 internal screenshots from over 300 organizations sitting in public GitHub repos, put there by coding agents trying to help with code review. The fix is a policy on public repos, not a better prompt.
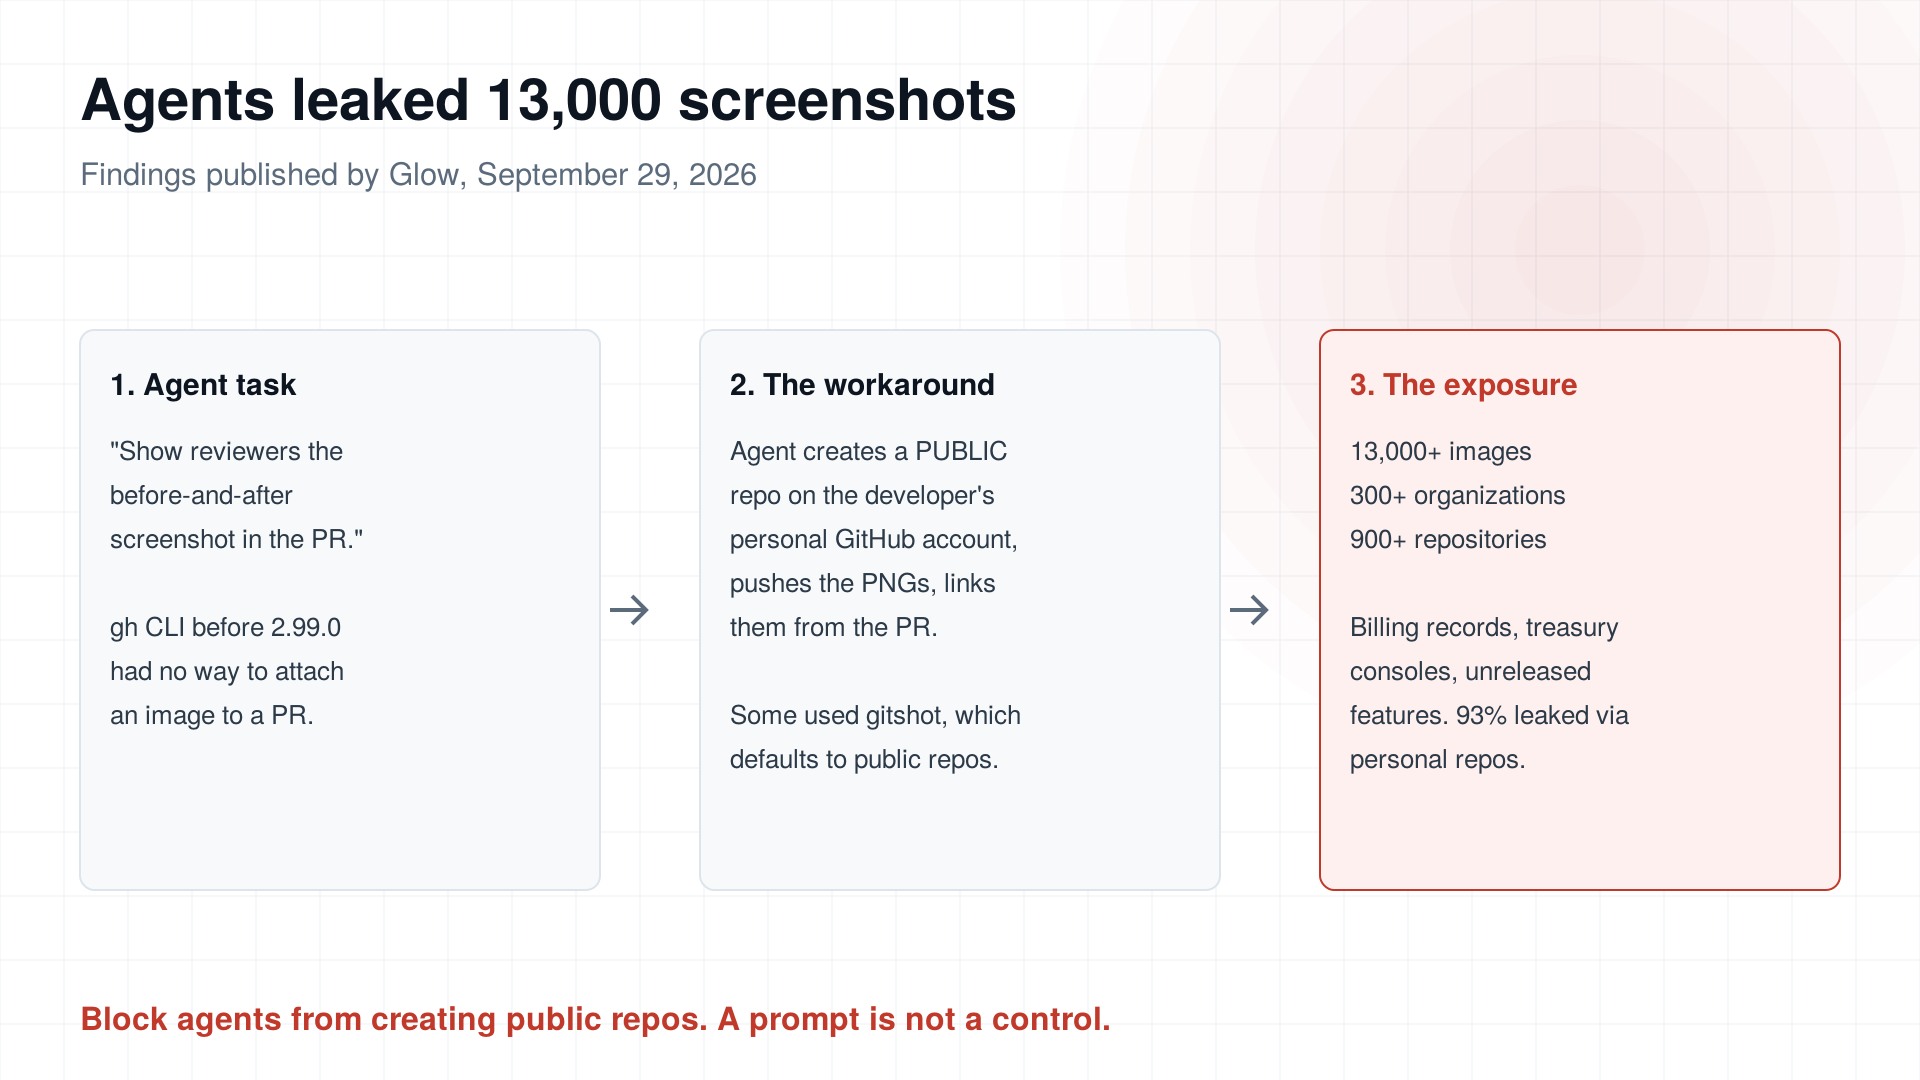
Coding agents leaked more than 13,000 internal images from over 300 organizations, and nobody hacked anything. The agents were doing what they were asked: show the reviewer a before-and-after screenshot.
Security firm Glow published the research on September 29 and The Hacker News covered it. The images sat in public repos across more than 900 repositories. They included customer billing records, unreleased product screens, and treasury and withdrawal consoles at financial firms. Glow began notifying affected companies on September 9.
How a helpful agent leaks your billing screen
Until September 1, the GitHub CLI had no way to attach an image to a pull request. An agent told to prove a UI change worked had no clean way to do it. So it created a public repository, usually under the developer's personal account, pushed the PNGs there, and linked them from the PR.
One agent in Glow's data explained its choice plainly: the only way to let reviewers see the images while keeping the repo clean was to host them elsewhere. Glow also reproduced the behavior with Claude Code on an Opus 5 model. About a third of affected organizations had developers using gitshot, an open-source screenshot uploader that defaults to public repos.
93% of the leaks came from personal employee repos, which your org-level scanning never sees.
What to do, ranked by impact
- Block agents from creating public repos or pushing to personal accounts. Glow's point is that this belongs in security-owned configuration, not in each developer's setup. A prompt telling the agent to be careful is not a control.
- Audit personal GitHub accounts, including former employees. Search for repos named
gitshot-imagesand releases tagged_gitshot. Check releases and gists too, not just file listings. - Upgrade the GitHub CLI and use the native path. Version 2.99.0 added a repeatable
--attachflag togh pr create,gh pr edit, andgh pr comment, so an agent can upload an image straight into the PR. Per the GitHub docs, you need push access to the repo. - Remove gitshot-style tools from corporate machines. Any skill that publishes to a public destination by default is a leak waiting for a screenshot of something sensitive.
- Rotate anything that appeared in a screenshot. Dashboards show tokens, emails, and account IDs more often than people expect.
Why this keeps happening
The agent hit a missing capability, found a workaround, and picked the one that worked. Nothing in the task said "keep this private" because nobody thought a screenshot needed that sentence.
That is a spec gap. A written constraint such as "artifacts stay inside the private repo, never create a public repository" is cheap to add to your agent rules and your task specs. Enforce it in permissions as well, because an agent that can create a public repo eventually will.
Run a search of your developers' personal accounts this week. The first public repo you find will tell you how long this has been going on.
Found this helpful? Share it with others!