OpenCode Got Breached and Your AI Bill Paid for It
Attackers reached a legacy system at OpenCode and exposed provider API keys stored in its hosted Console, and users are reporting hundreds of dollars in unauthorized charges. The lesson is about where you keep your keys, and the fix takes ten minutes.
If you gave OpenCode your OpenAI, Anthropic, or Google key through its hosted Console, go revoke that key now. Then read the rest.
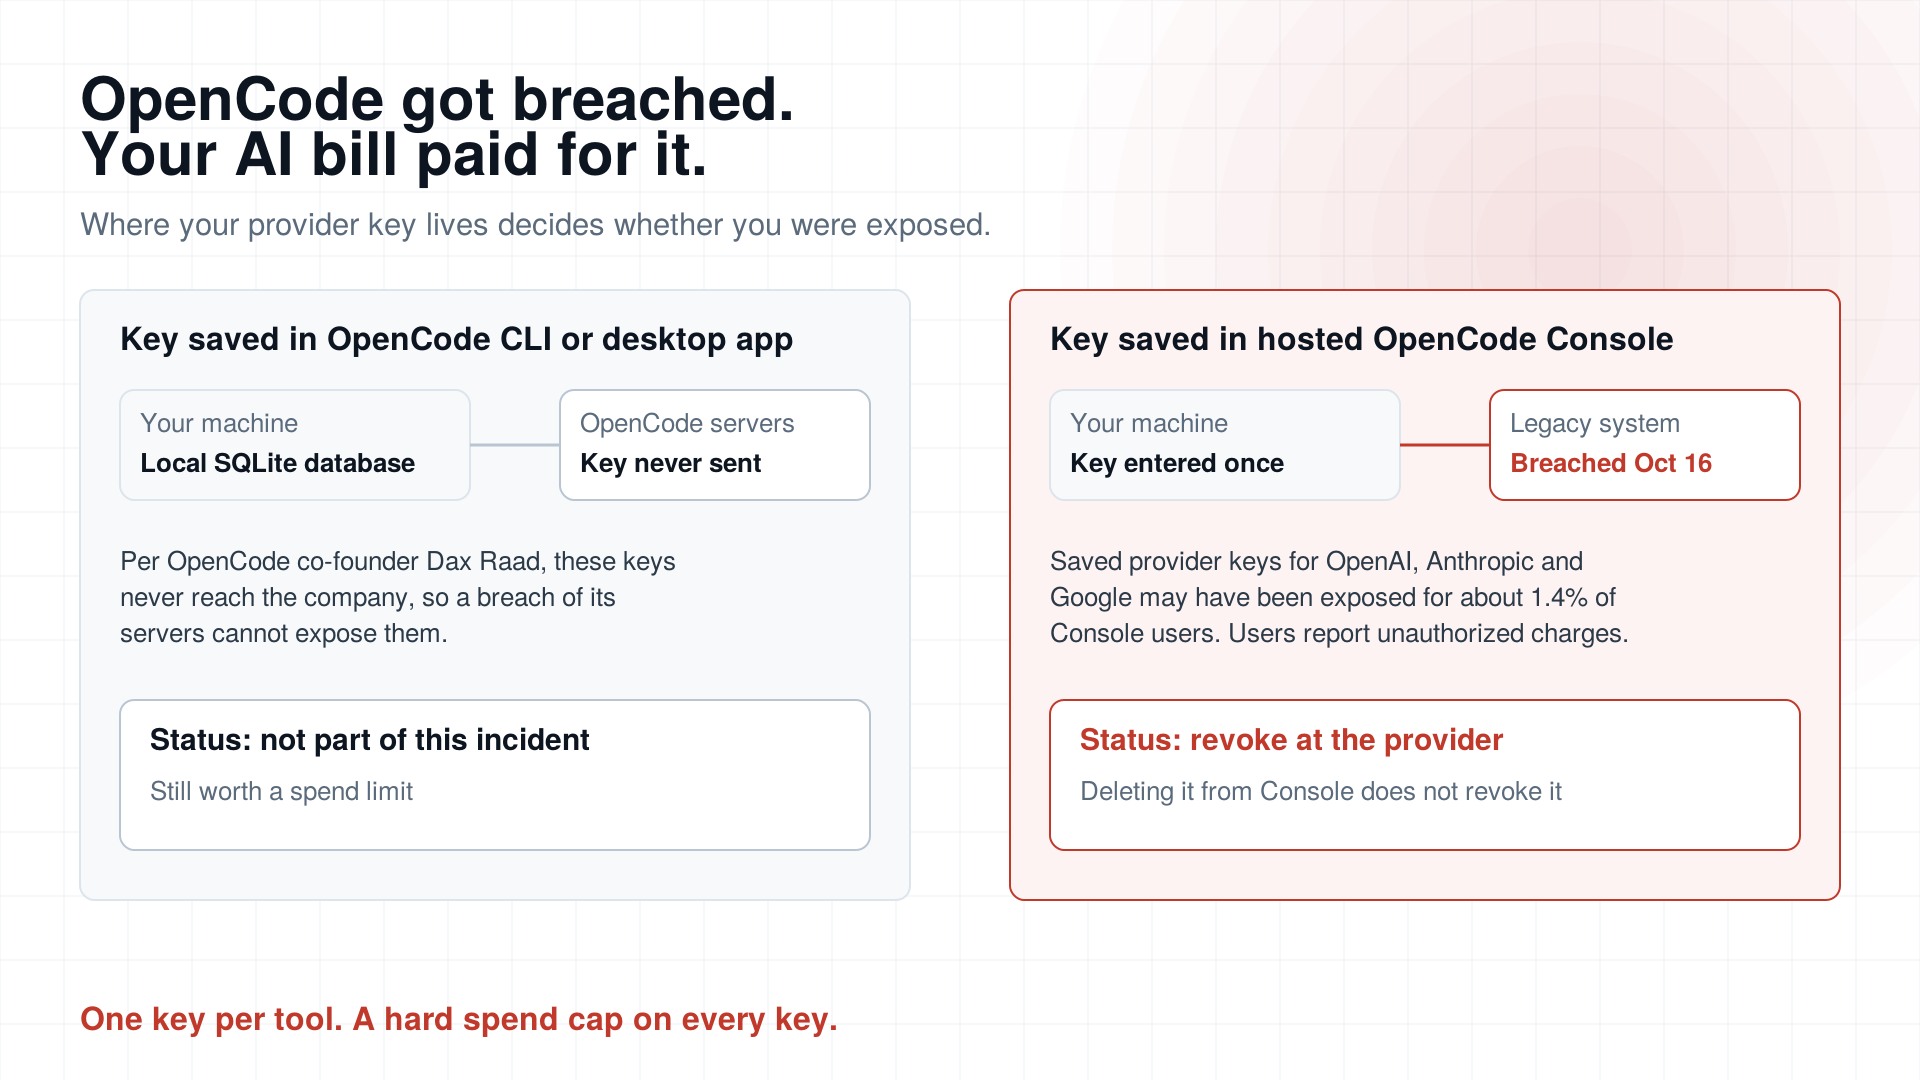
According to TechCrunch and The Hacker News, an intruder reached a legacy OpenCode system on the night of October 16. About 1.4% of Console users were affected, and OpenCode emailed them on October 17 with the subject "Action Required: Potential provider key breach."
What actually happened
Console is an optional hosted service where a team saves a provider key once so members can use models without seeing the key. Those saved keys are what was exposed. Keys entered in the OpenCode CLI and desktop apps live in a local SQLite database, and co-founder Dax Raad says they never reach OpenCode's servers.
Users are reporting unauthorized charges across all three providers. One developer posted $281 on OpenAI and $168 on Anthropic, another reported around $400 on Anthropic, and one said losses reached about $1,700. These are user claims, and OpenCode has not confirmed that any keys were copied or used.
Anthropic and Google blocked the keys they believed were exposed, and OpenAI is working with OpenCode on refunds. OpenCode calls the incident ongoing, has not said how attackers got in, and has not said how many keys it held. It describes the event as a "large-scale distillation attack" without explaining the link, and some observers call that framing a stretch.
What to do today
Ranked by how much damage each step prevents:
- Revoke the key at the provider. Deleting it from Console does not revoke it. Go to the OpenAI, Anthropic, or Google dashboard, kill the key, and issue a new one.
- Check usage back to October 16. Look for requests you did not make and file for a refund through the provider.
- Set a spend limit. Anthropic and OpenAI both document spend limits. A capped key turns a $1,700 incident into a $50 one.
- Issue one key per tool. When a tool is compromised, you rotate one key instead of rebuilding every integration.
- Update every script that used the old key. Old keys hide in CI secrets and dotfiles, and they fail quietly after revocation.
The part vendors will not say
Every hosted layer that stores your provider key is a second place to get breached, and you do not control its security. A team that pastes a shared key into a third-party console has handed that vendor the ability to spend its money.
Local-only key storage, per-project keys, and hard spend caps are boring controls. Those three would have limited this entire incident.
Audit every AI tool your team uses this week and ask where it keeps your keys. If the answer is "on their servers," cap that key before you find out the hard way.
Found this helpful? Share it with others!